Identity: who is acting?
Identity establishes the person, workload, service, or agent involved. It supports authentication, accountability, and policy assignment. This is foundational.
Access: what can it reach?
Authorization defines resources and capabilities available to that identity. Good access design narrows the possible action space, but does not necessarily describe the exact operation the agent is about to perform.
Runtime: what is about to happen?
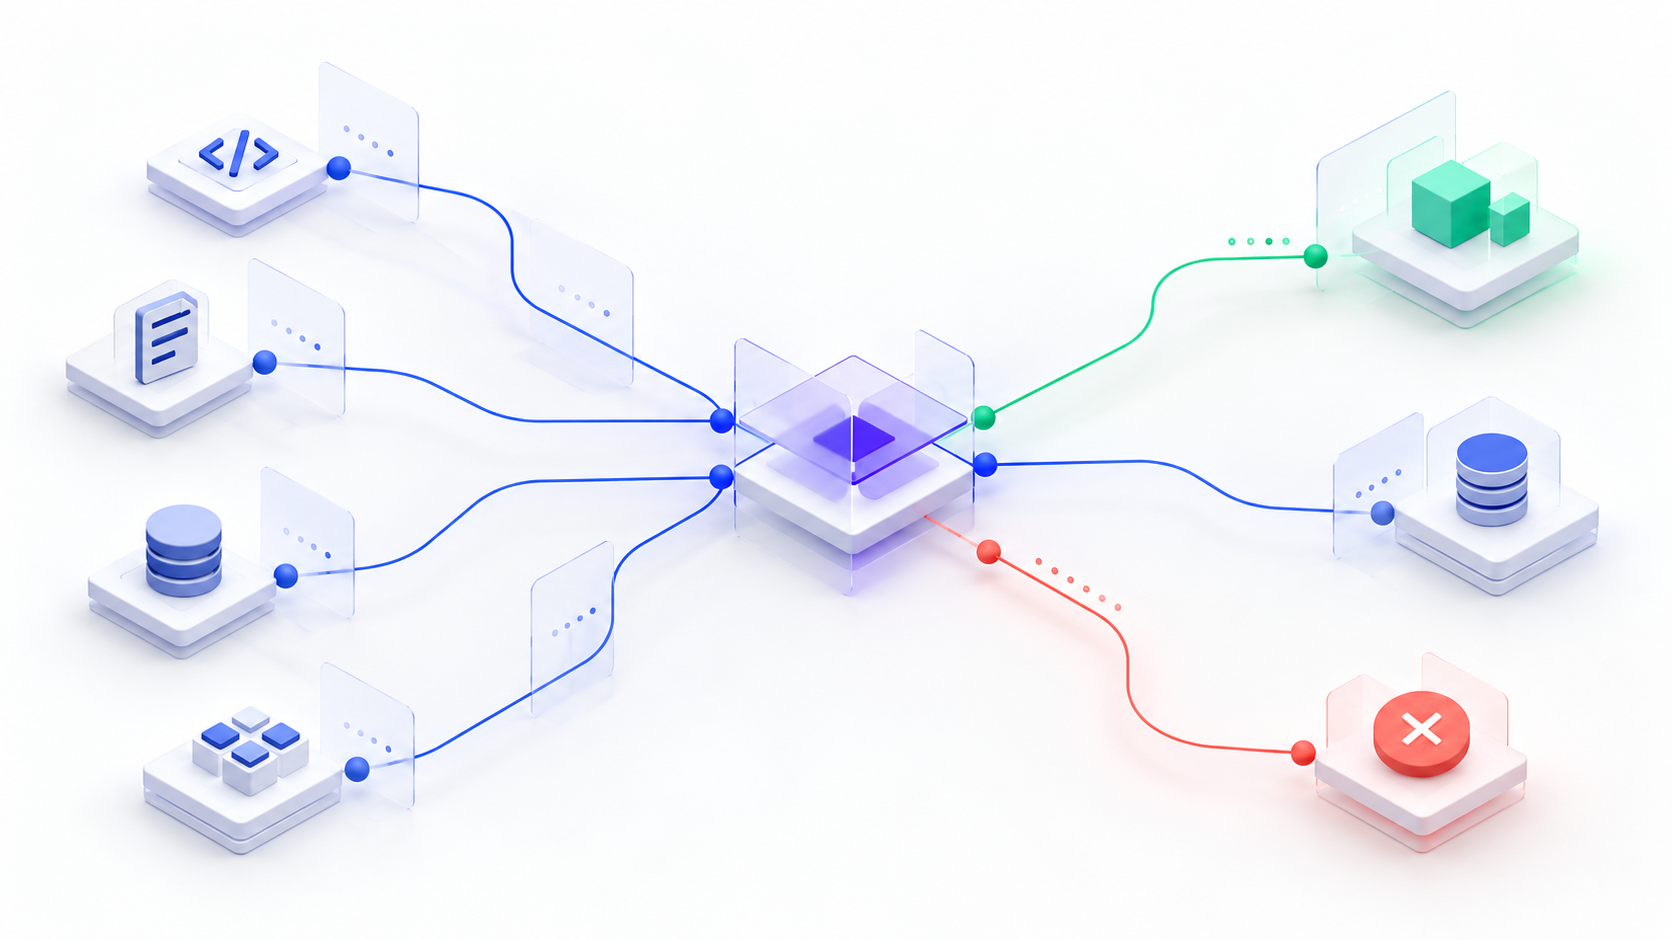
Runtime control evaluates the concrete supported action as it approaches execution, such as a command, package operation, tool call, or external service request.
One architecture, three questions
Identity can establish the actor, access can constrain reach, and runtime control can evaluate behavior. The right mix depends on the architecture and risk. None is a universal substitute for the others.